Moose Infotech Editorial Team · 3 min read
Published
Define the tenant boundary
A tenant might be a company, a business unit or an independent customer account. Decide how users belong to tenants and whether someone can belong to more than one. These choices affect invitations, permissions, billing and reporting.
Document the data each tenant owns and any genuinely shared records. Shared reference data should not become an accidental route to customer information. Tenant identity must be established through trusted application context, not accepted blindly from a user-supplied field.
Choose a model with lifecycle costs in mind
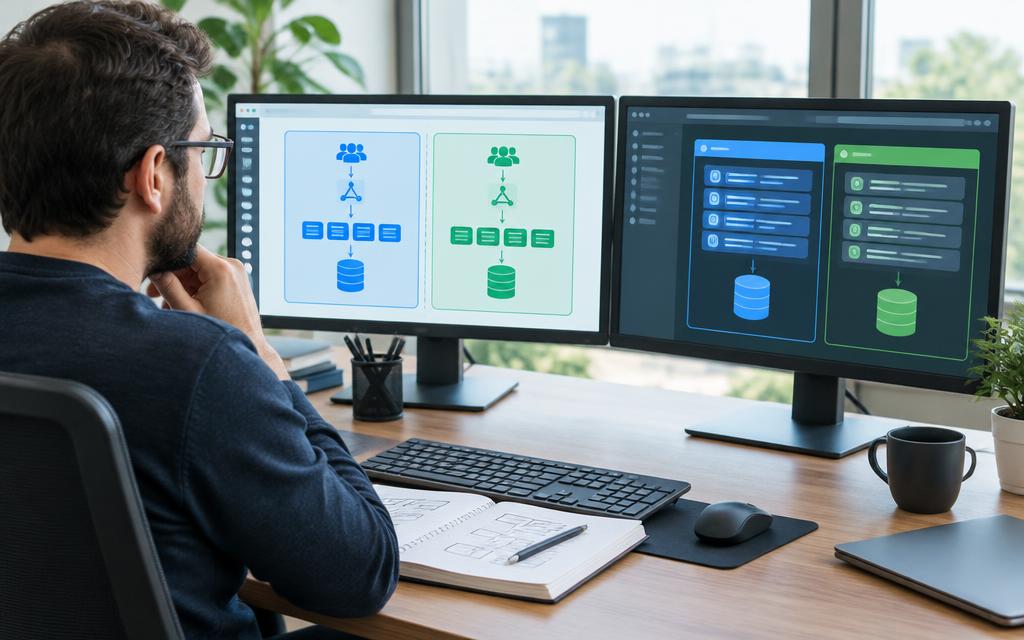
Shared tables, separate schemas and separate databases have different operational tradeoffs. Compare access controls, migration effort, backup and restore, reporting and the level of isolation required by the business. No model is automatically correct for every SaaS product.
Include the cost of operating the model as tenant counts grow. A separate database per customer may simplify some boundaries while adding provisioning and maintenance work. A shared database needs consistent tenant-aware controls and strong tests.
Protect more than database queries
Files, caches, search indexes, queues and exports also carry customer data. Include tenant context in their design and enforce authorization at access time. Avoid cache keys or file paths that can collide across customers.
Background jobs should preserve the correct tenant context and permissions. A job created by one tenant must not process another tenant's records because a default or missing identifier was accepted. Test retries and delayed jobs after account permissions change.
Control administrative access
Support and platform administration may require broader access than ordinary users. Define who can exercise it, why it is needed and how actions are recorded. Keep privileged credentials on the server and verify permissions before using them.
Avoid granting authority based on profile fields users can edit. If staff can impersonate a customer for support, design explicit approval, audit and exit behavior. Convenience features should not erase accountability or expose another organization's information.
Test isolation with adversarial scenarios
Create at least two tenant accounts with similar-looking records and different roles. Attempt access by changing identifiers, replaying requests and opening shared links. Include exports, attachments and API endpoints rather than only visible screens.
Test membership removal and invitation changes. Verify that an account losing access cannot still retrieve cached files or continue a privileged action through an old session. Automated regression tests help keep these boundaries intact as features are added.
Plan recovery per customer
Determine how a customer's data can be exported, restored or removed without affecting other tenants. Document the limits of your backup model and retention policy. Tenant isolation is a product and operations concern as well as an architecture decision; it must hold throughout the customer's lifecycle.