Moose Infotech Editorial Team · 3 min read
Published
Define the release risk
A release that changes an informational page has a different risk profile from one that changes billing or access permissions. Identify who is affected, what can go wrong and how quickly a problem must be detected. Match the review effort to that risk.
Agree the minimum evidence required to proceed. A low number of open bugs can be misleading if testing did not cover the critical workflow. One unresolved authorization defect may matter more than many cosmetic issues.
Test complete user journeys
Cover the path a real user follows: entry point, authentication where required, input, confirmation and the ability to read the result back. Use representative data and permissions. Test invalid input, repeated submissions, interrupted requests and empty states.
For illustration, an inquiry form is not ready just because it displays a thank-you message. Verify that the submission was stored, that an appropriate notification was triggered and that failure does not produce false success. Apply the same principle to purchases, approvals and account changes.
Include devices and accessibility
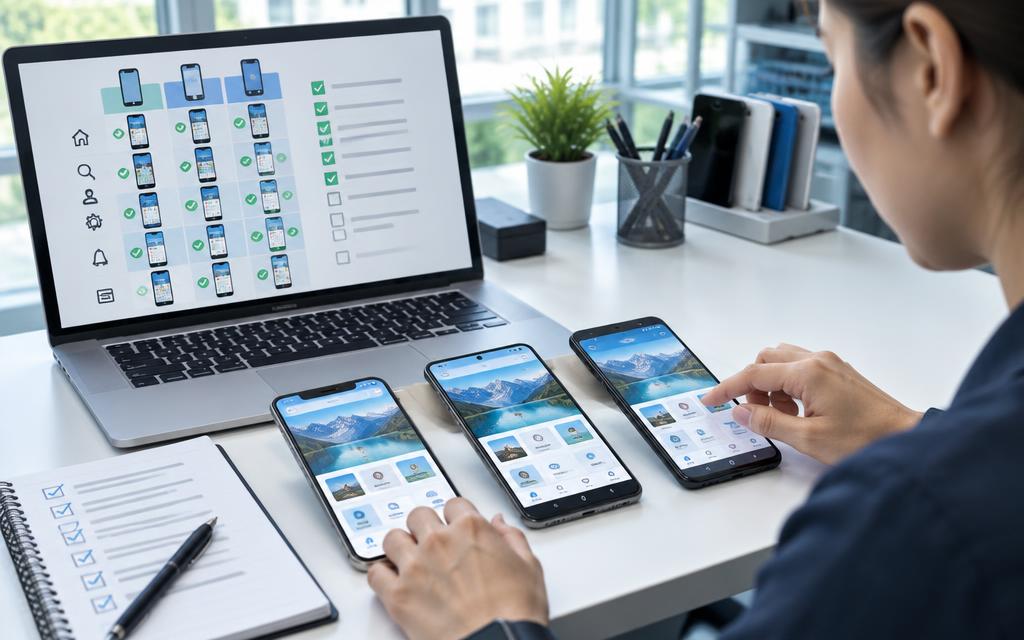
Check common phone, tablet and desktop widths, along with narrow layouts and text zoom. Inspect menus, long titles, tables and form errors. A page with hidden horizontal overflow can still have clipped controls.
Use a keyboard to complete important actions. Verify labels, focus order, visible focus and announced error or success states. Automated checks can identify some problems, but manual interaction remains necessary for understanding whether the workflow is usable.
Verify security and recovery behavior
Test whether each role can perform only its permitted actions, including direct requests outside the visible interface. Check that sensitive values do not appear in logs or analytics. Review the effect of changed dependencies and environment settings.
Document how the previous version can be restored and whether a data migration can be reversed safely. Some migrations need a forward repair rather than a simple rollback. Rehearse the recovery path appropriate to the change instead of assuming redeployment will solve every issue.
Make production signals actionable
Agree which errors and workflow outcomes will be monitored, who receives alerts and what action they should take. Avoid collecting unnecessary personal data. A useful signal identifies an operational problem without exposing the contents of a customer's request.
Verify that the support team can distinguish an application failure from a delayed external service. Prepare a short issue-triage guide and identify the release owner. Monitoring that nobody reviews provides little protection.
Record the decision and follow up
A readiness review should conclude with evidence, accepted risks, unresolved blockers and named owners. After deployment, repeat the central workflow in the real environment and confirm the result. Treat readiness as an operational decision, not a checklist that ends when the software compiles.